Network Design
We engineer resilient, high-performance network architectures tailored to keep your business connected, secure, and ready to scale. From seamless cloud integration, SD-WAN, SASE to airtight firewall policies and zero-downtime routing, we design infrastructure built for maximum uptime and effortless management.
Servers and Backups
We proactively manage and protect your servers using automated security patching, real-time 24/7 threat monitoring, and hardened access controls. Coupled with immutable backups and rapid disaster recovery, we ensure your critical business data remains fully protected and quickly recoverable.
Defensible Architecture
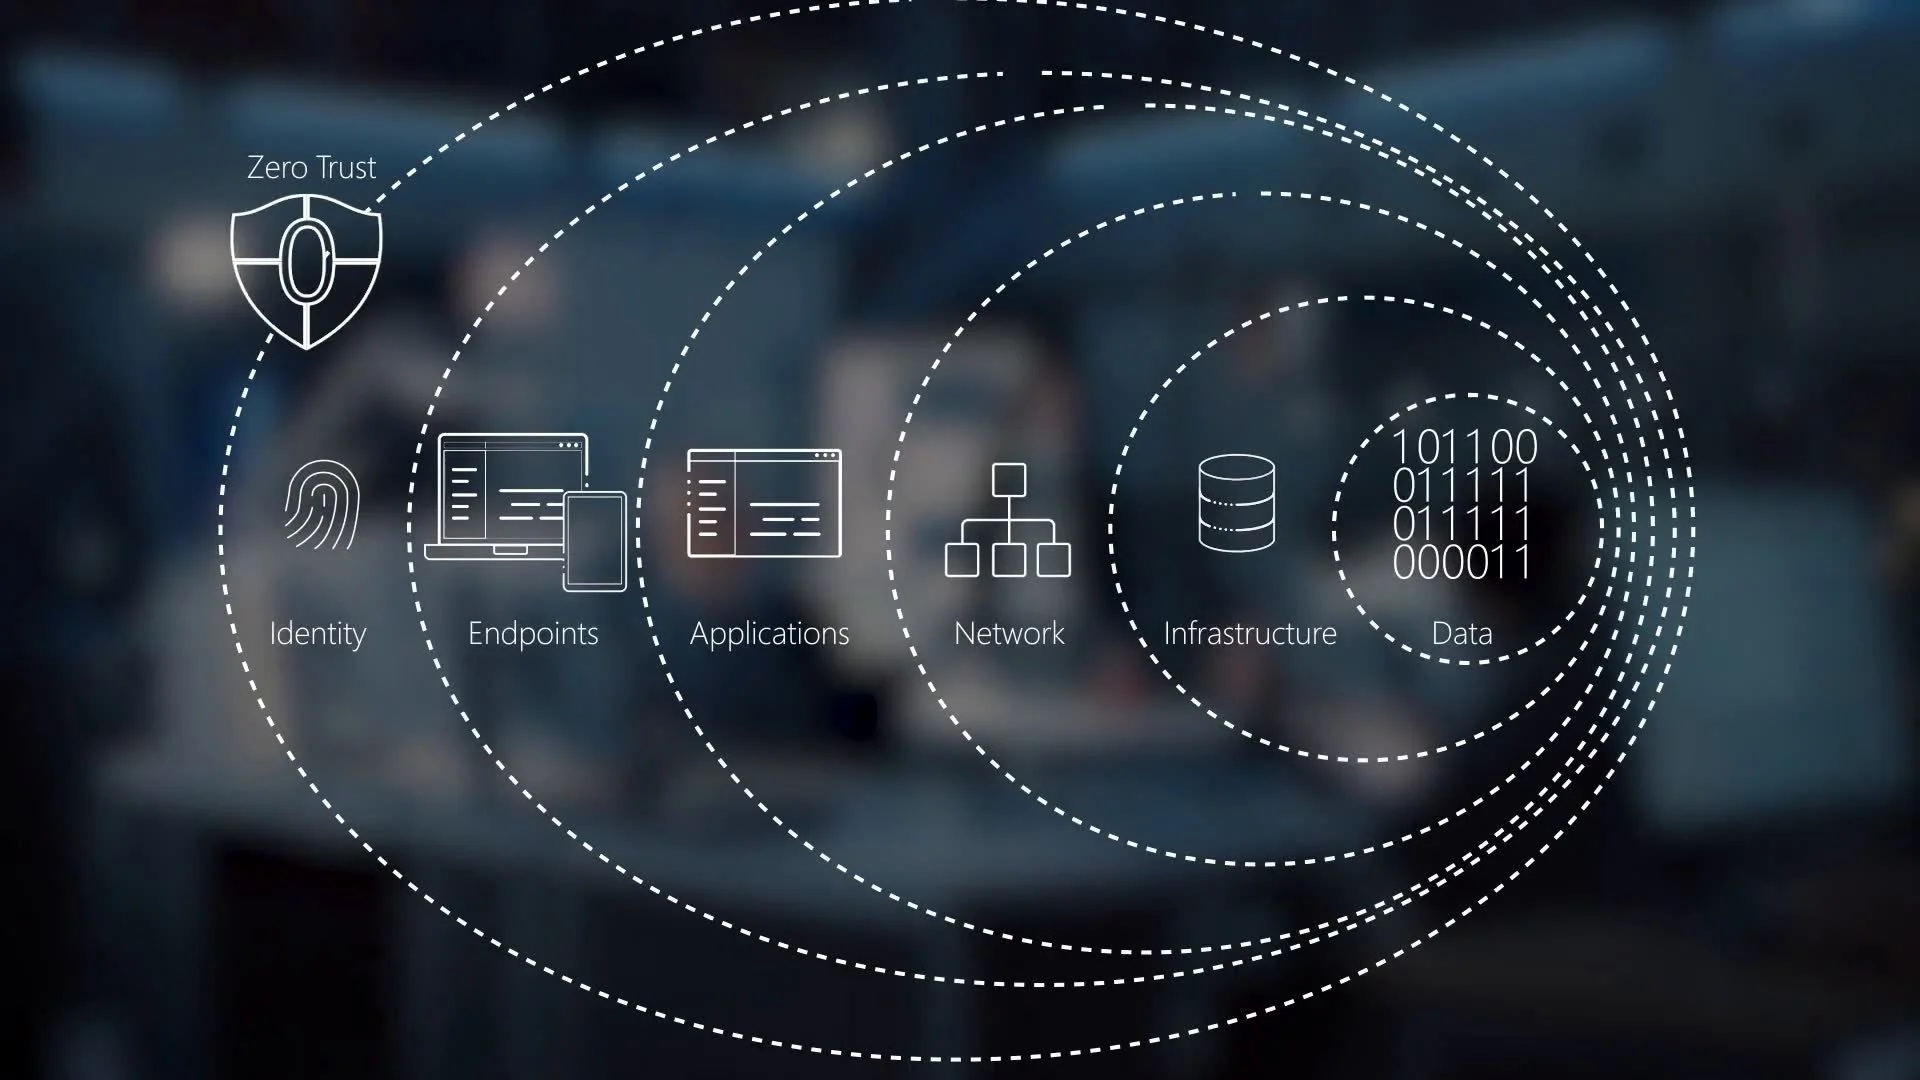
We replace outdated perimeter-based security with continuous, identity-driven verification across every user, device, and network transaction. Using Zero Trust Architecture we can implement micro-segmentation, strict least-privilege access, and automated threat containment, we ensure your critical assets stay protected—no matter where your workforce connects from.
HIPPA
FFIEC
PCI-DSS
NIST
Managed Infrastructure
Managed Servers “Foundation”
Continuous updating and patching of the operating system.
Key resource monitoring and monitoring uptime.
24/7 continuous threat monitoring and response by a dedicated Security Operations Center (SOC).
Backup remediation and assistance in case of disaster recovery.
Managed Switches “Paths”
VLAN Architecture & Traffic Isolation for granular network segmentation and access control.
Spanning Tree Protocol (STP) & Loop Protection to ensure topology stability and zero-down-time failover.
802.1X Port Security & Access Control to prevent unauthorized physical device onboarding.
Quality of Service (QoS) & Prioritization for critical real-time traffic like VoIP and video.
Firmware Maintenance & Port Provisioning upon request, with 24/7 port and link state monitoring.
Managed Firewalls “Fortress”
Perimeter Threat Protection Rules, Policy Optimization, Threat Intelligence Logging, and High-Availability Clustering.
Remote VPN and VPN tunnel management and altering of failures.
Firewall rule changes upon request.
Automatic priority 1 on outages, and 24/7 outage alerting.
Managed Routers “Roads”
Advanced Core & Edge Routing with OSPF, eBGP, and iBGP protocols.
Multi-Tenant Isolation and Traffic Segmentation via VRF Routing.
Control Plane Policing (CoPP) for CPU Protection and DDoS Mitigation.
High-Availability Failover, Path Redundancy, and Dynamic Tunneling.
Automated Priority 1 Incident Response for Core Link & Device Outages with 24/7 Monitoring.